Статті та ресурси
Практичні матеріали про безпеку вбудованих систем, найкращі практики IoT і регулювання CRA
ENПоки що наші статті виходять англійською. Українські версії готуємо.
Ми відкрили нашу базу знань про CRA, RED, NIS2 і CSA
Один репозиторій про всі правила ЄС, що стосуються безпеки електроніки та IoT: з перевіреними фактами, структурований і безкоштовний за ліцензією CC BY 4.0. Встановіть його як Claude Skill і питайте напряму, які правила стосуються вашого продукту. Матеріали англійською.
Відкрити репозиторій на GitHub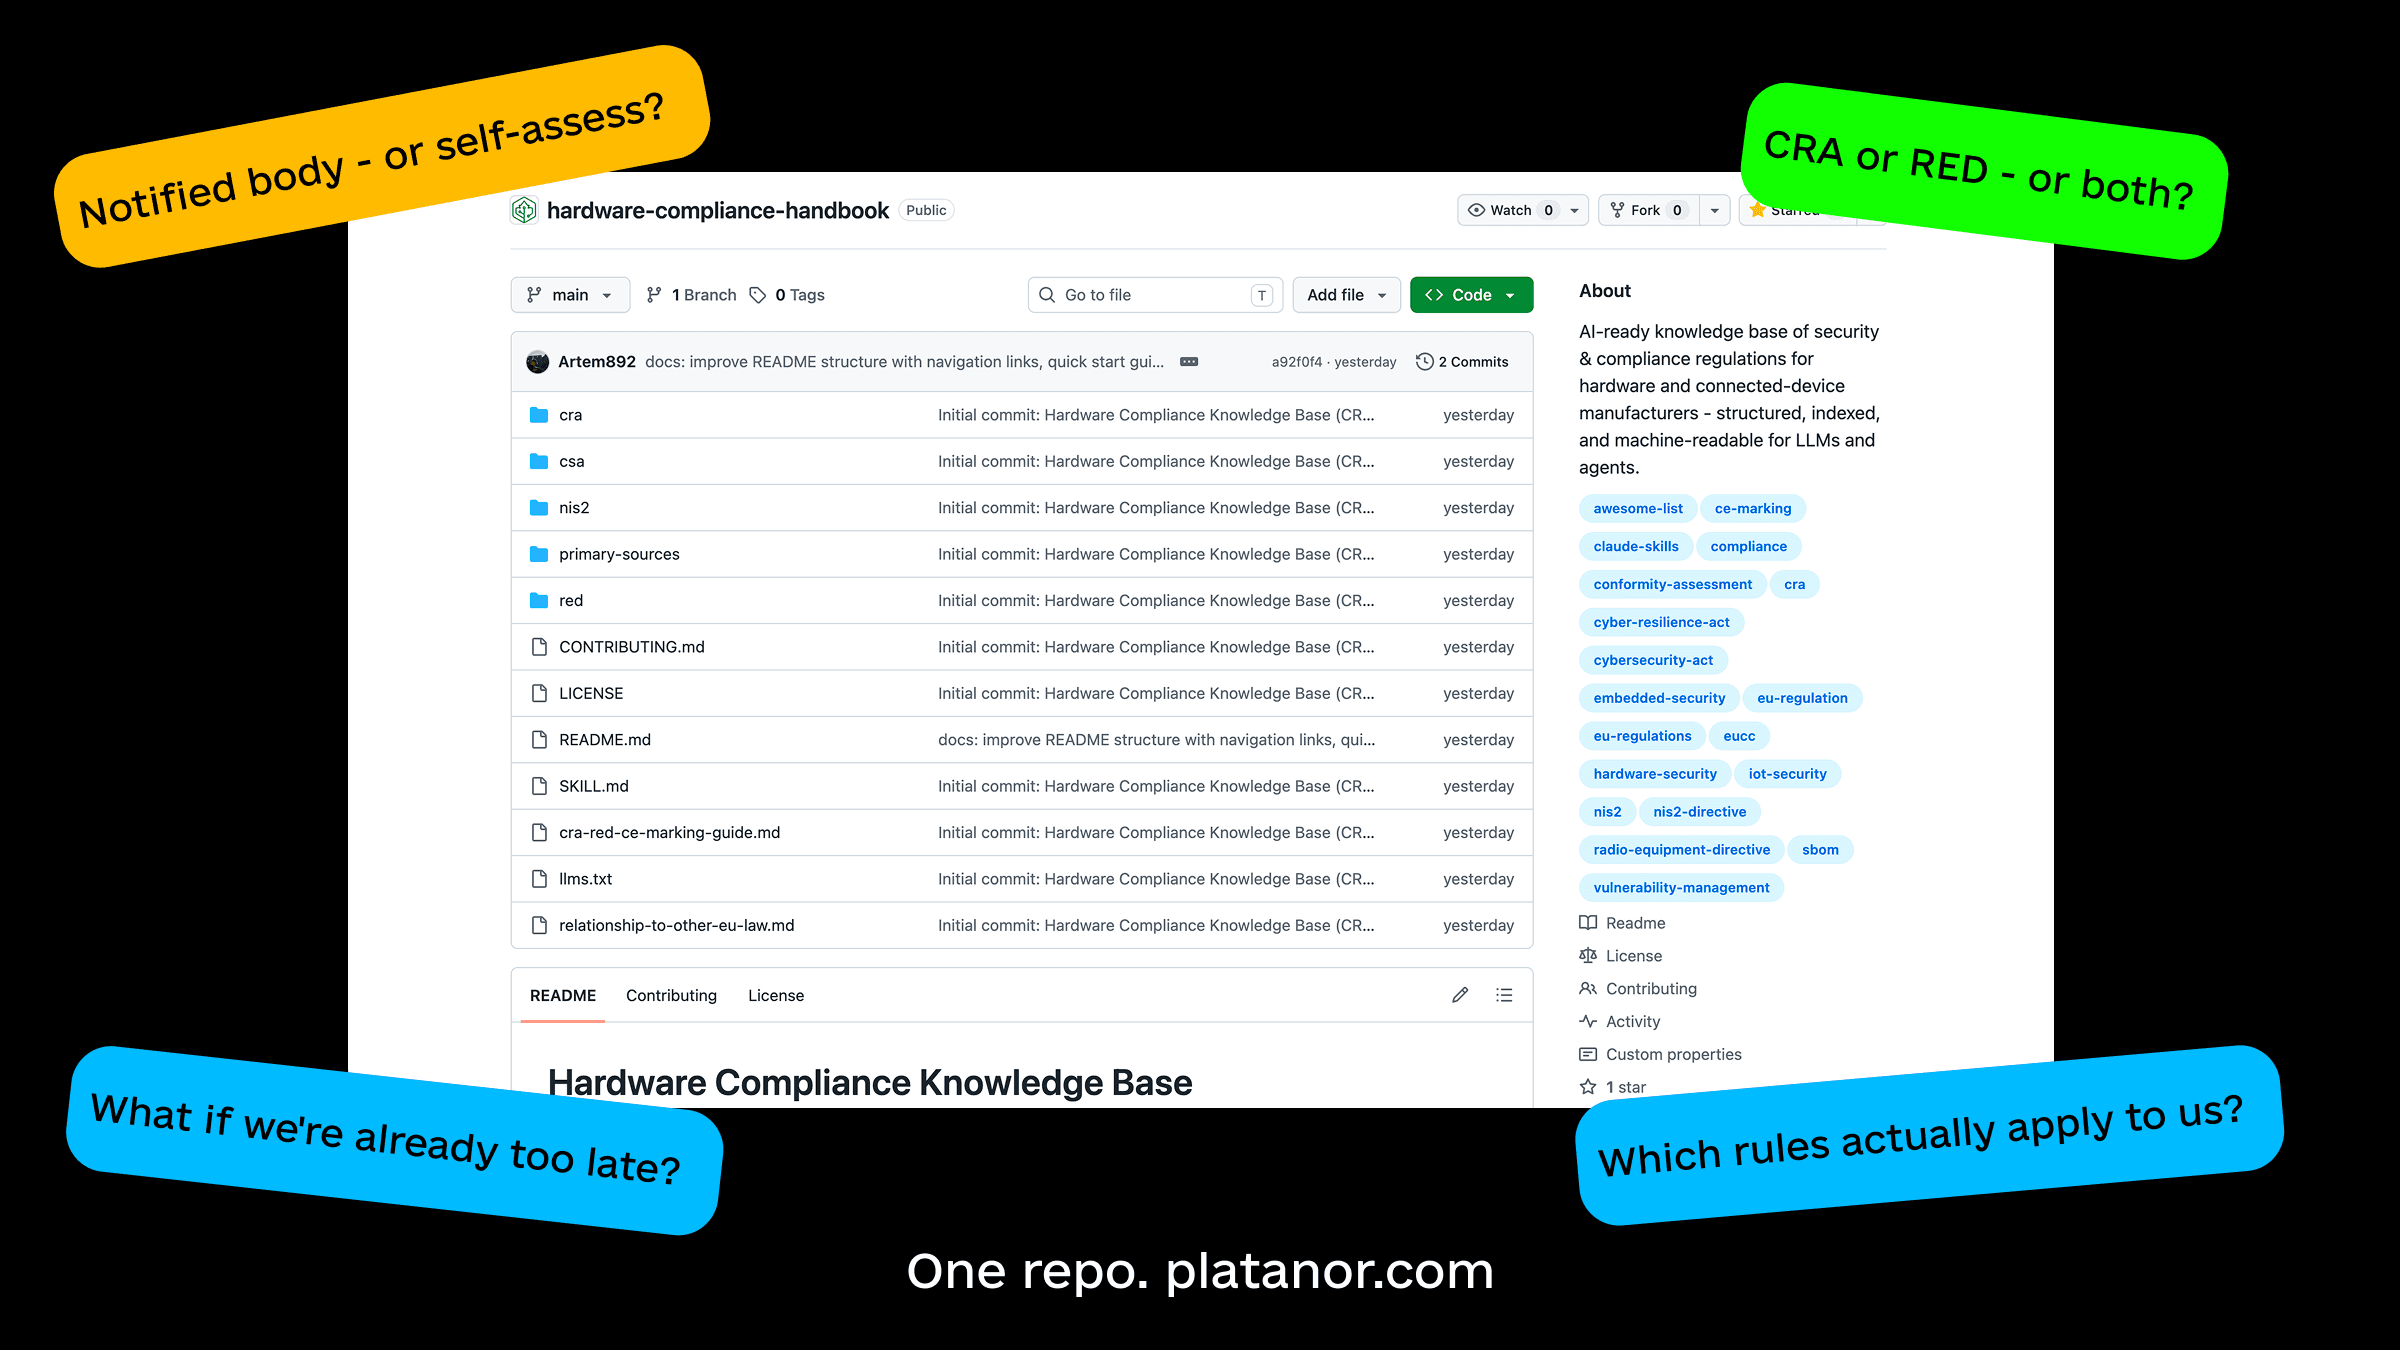
What Is a CVE? A Practical Guide to Vulnerability Tracking for IoT Manufacturers
A CVE is a standardized ID for a known vulnerability - but for an IoT manufacturer, tracking which ones apply to your product is the hard part. What a CVE is, how the system works, and how to build a CVE tracking process that doesn't fall apart at scale.
CE Marking for Connected Devices: A Practical Step-by-Step Guide to CRA and RED Compliance
CE marking isn't one stamp - it's the visible outcome of separate CRA and RED assessments running in parallel. A step-by-step walkthrough of self-assessment: product classification, technical documentation, Module A, the EU Declaration of Conformity, and the post-market duties that start once the mark goes on.

Security by Design: The CRA Requirement With No 'Where Applicable' Clause
Every requirement in CRA Annex I, Part I comes qualified by 'where applicable' - except one. Point 1 has no escape clause, and it is not really a control you can check off. Here is what that means for how you design a product, and why waiting until 2027 to start is already too late.
CE Marking and the CRA: What the Mark Certifies - and What It Does Not
Most manufacturers assume a CE mark means someone tested their product and approved it. It does not. Under the CRA the mark is a declaration you sign yourself, and it is not a second mark on top of the one your device may already carry under RED. Here is what it means, and when it starts to matter.
What Is Device Identity in IoT - and What CRA Actually Requires
CRA does not mandate device identity by name. But on a fleet of identical devices it is the most defensible answer to the access control requirement in Annex I. Here is what it actually means for IoT manufacturers, what the regulation does and does not say, and how to add it without a redesign.
IoT Threat Modeling: A Step-by-Step Guide for Hardware Manufacturers
Learn how to build a threat model for your IoT device using STRIDE. A practical step-by-step guide for hardware manufacturers preparing for EU CRA compliance.
CRA Article 14: Vulnerability Reporting Obligations Starting September 2026 — What Manufacturers Must Prepare Now
CRA Article 14 mandatory vulnerability reporting starts September 11, 2026. What IoT and hardware manufacturers must have in place technically and operationally before the deadline.
Secure OTA Updates for IoT Devices: What Can Go Wrong and How to Build It Right
Unsigned OTA updates are one of the most common IoT security failures. Here is what a correct secure firmware update architecture looks like - and what CRA requires from it.
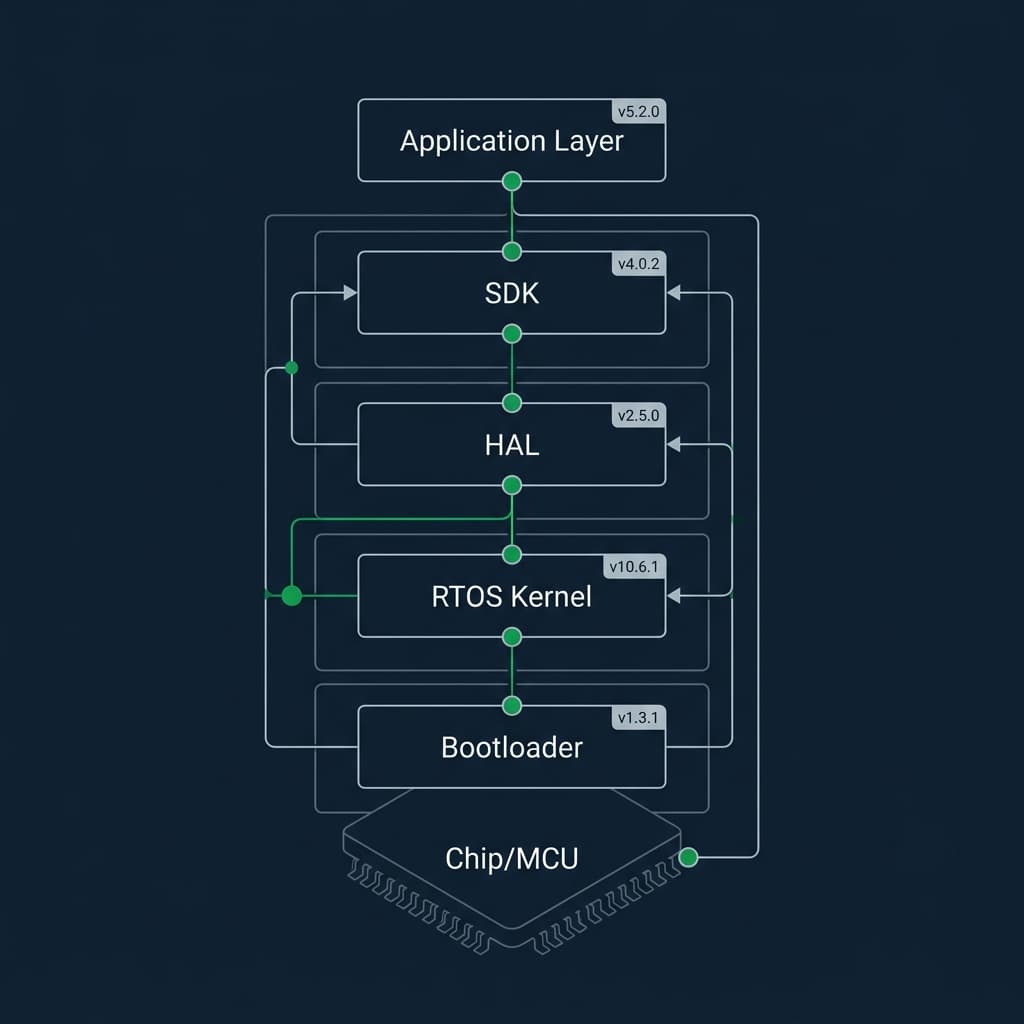
SBOM for IoT Manufacturers: What CRA Requires and How to Create One
CRA requires an SBOM for every connected product. Here is what it must contain, which format to use, how to generate it for embedded firmware, and how to keep it current post-release.
June 11, 2026: What This CRA Milestone Actually Starts for Manufacturers
On June 11, 2026, the EU activated the legal rules for building its CRA conformity assessment infrastructure. What this milestone means for IoT and hardware manufacturers - and why the window to prepare is closing.
What is Secure Boot - and Why Every IoT Device Needs It
Secure boot verifies that your device runs only firmware you signed. Here is how it works, why CRA treats it as a baseline requirement, and what a correct implementation looks like on Nordic nRF and STM32.
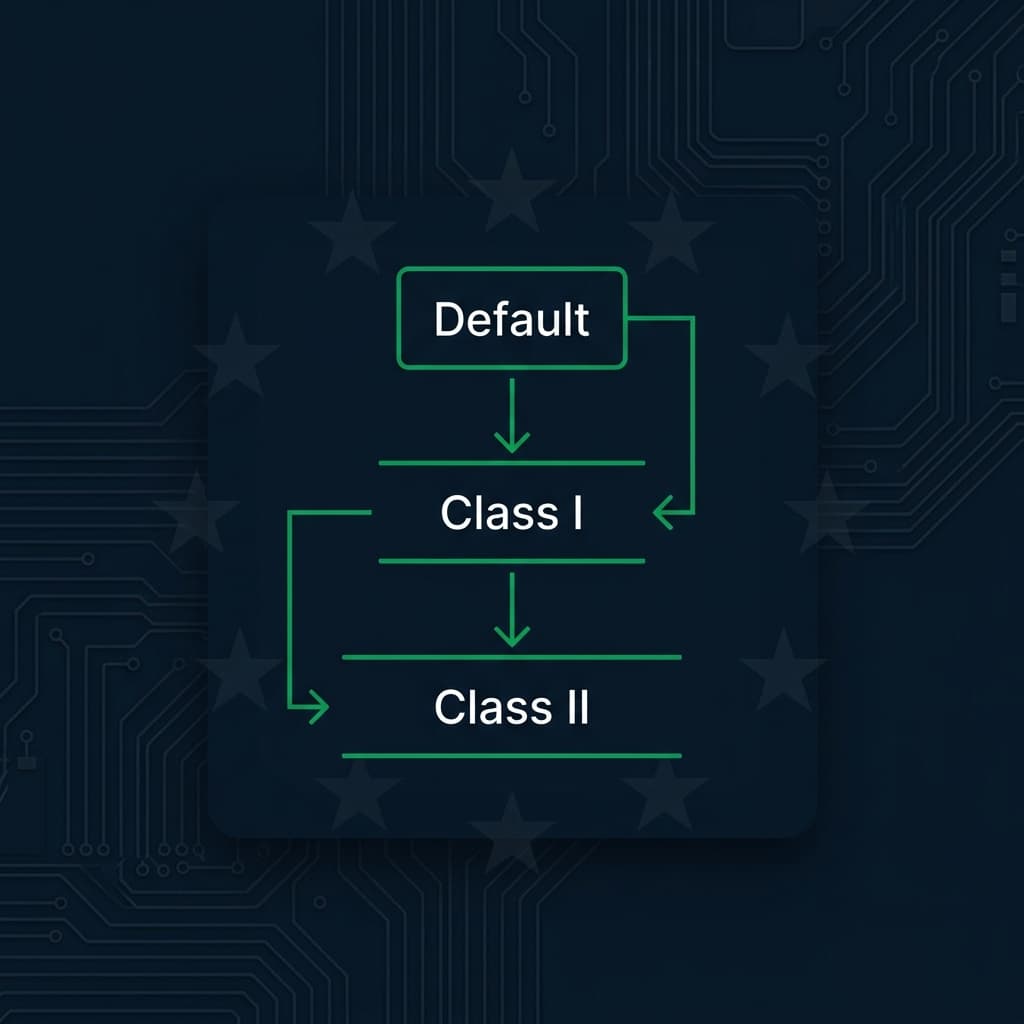
How to Classify Your Product Under CRA: Default, Important Class I, or Class II
Your CRA product category determines your entire compliance path. Here is how to correctly classify your IoT or hardware device under the Cyber Resilience Act - and why getting it wrong costs time and money.
September 11, 2026: The First CRA Deadline Most Manufacturers Are Not Ready For
September 11, 2026 is the first binding CRA deadline - and it applies to products already on the EU market. Here is what the 24-hour reporting obligation requires and how to prepare.
EU Cyber Resilience Act: A Complete Guide for IoT and Hardware Manufacturers (2026)
The EU Cyber Resilience Act requires IoT and hardware manufacturers to comply by December 2027. Deadlines, requirements, SBOM, penalties up to €15M - complete guide by Platanor.